Role-based applications primarily depend on object structure security (though there is always a READ permission to determine whether you can see the application). The proper way to grant these is to use the Manage/Apply Template action in the Options section for the application in the Security Groups (Manage) application.
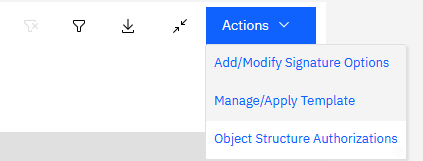
That will bring up a dialog where a security template should exist. From there you use the Actions->Apply Template
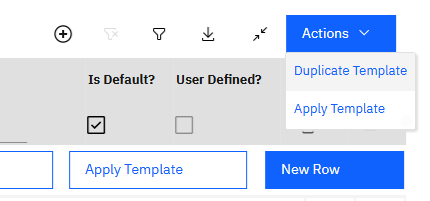
That will prompt a warning that you proceed through, and it will apply to the security group